This guide addresses a recurring failure reported in user forums: wiping the machine before checking every legitimate recovery-key location. The safe method is staged and verifiable. It begins with an inventory, protects the last working path, follows current official documentation, and tests the result before cleanup.
Quick scan
In brief
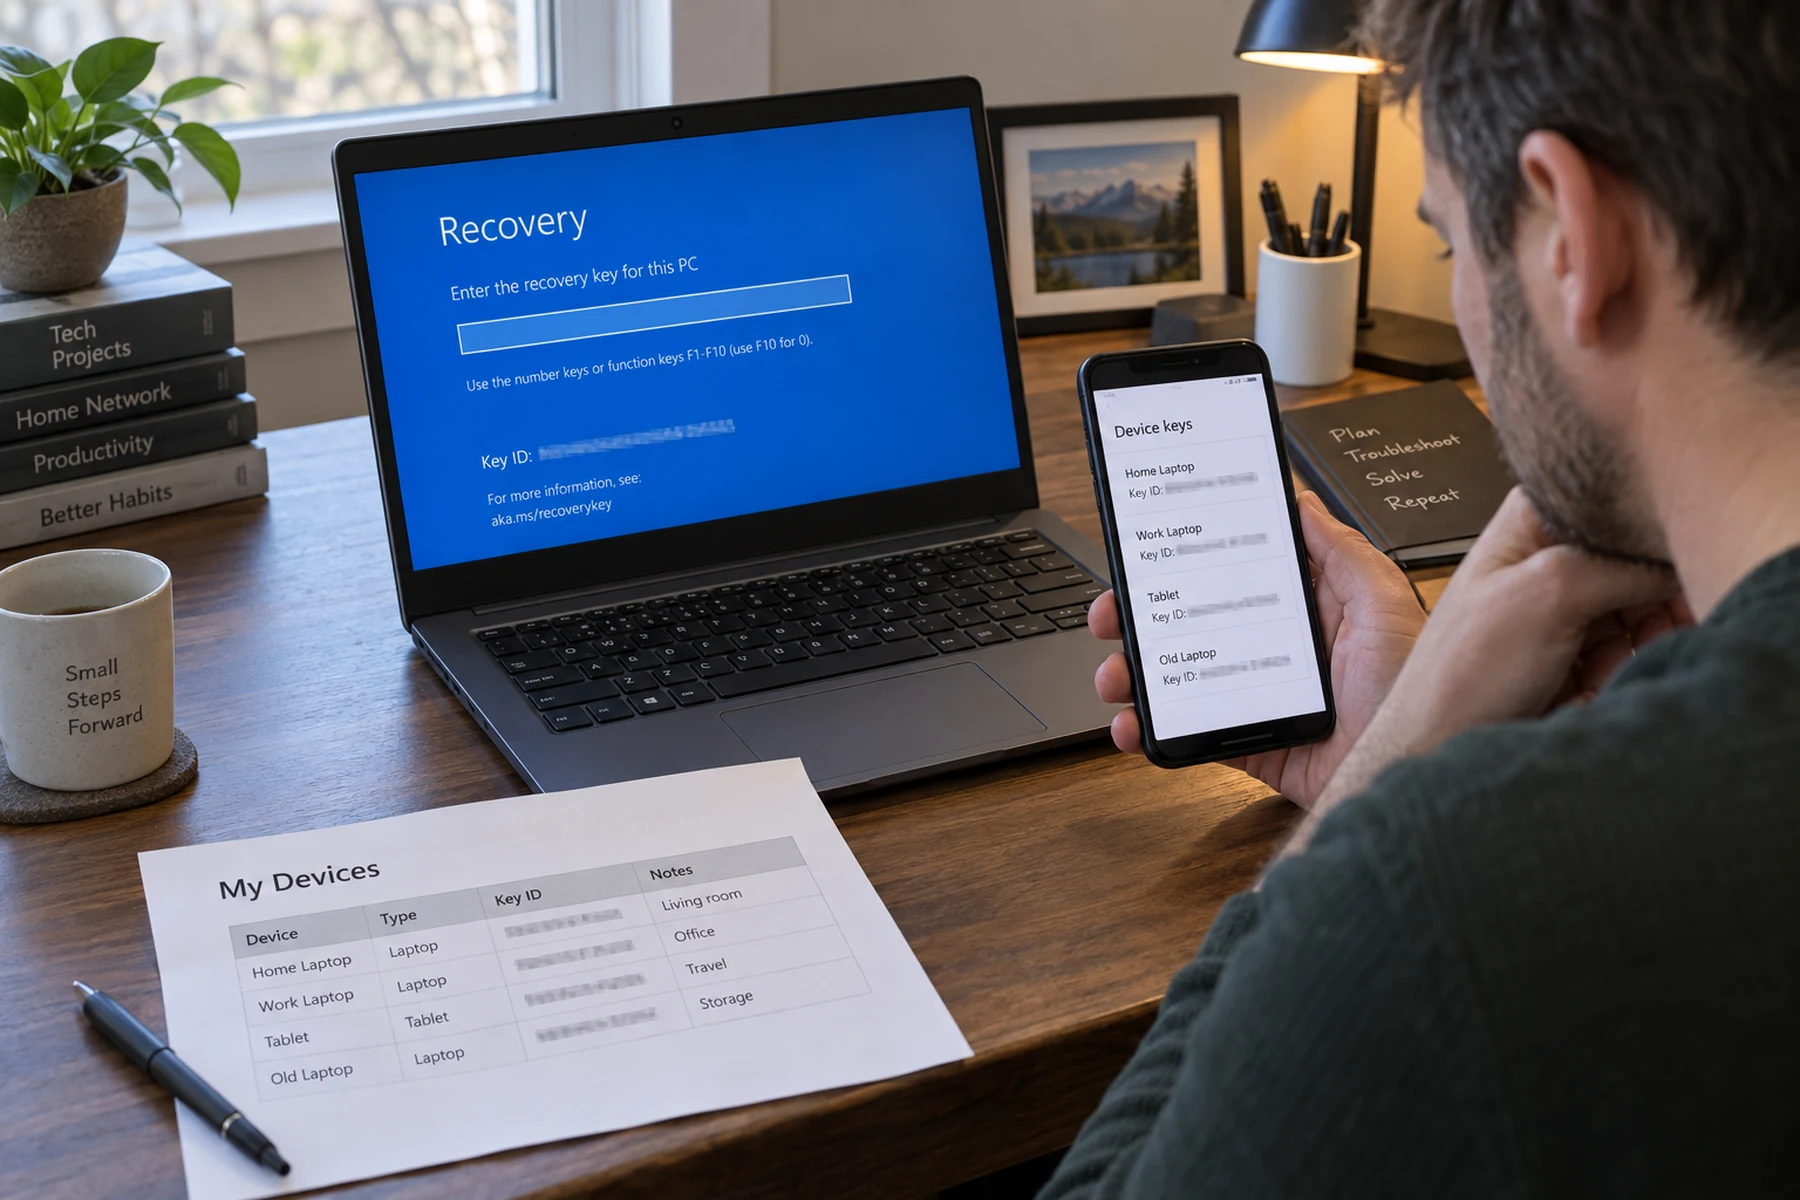
Photograph the recovery screen and record the key identifier and error code.
Match the identifier before entering a 48-digit key.
Do not clear the TPM or reinstall until data recovery and ownership are understood.
1. Photograph the recovery screen and record the key identifier and error code
A calm incident record begins with check the Microsoft account, work or school organization, printed copy, USB drive, and device-management records. Tie it to “1. Photograph the recovery screen and record the key identifier and error code” and to the intended outcome: regain access to the encrypted Windows installation without destroying the only copy of the data. Avoid a chronological diary of every click; preserve the few observations that change the diagnosis or next action.
Name the avoided error—wiping the machine before checking every legitimate recovery-key location—and the point where specialist help becomes safer than another attempt. Store the summary away from the affected device. That makes the next response start with a tested method instead of an anxious memory.
2. Check the Microsoft account, work or school organization, printed copy, USB drive, and device-management records
Finish “2. Check the Microsoft account, work or school organization, printed copy, USB drive, and device-management records” by proving both normal use and recovery. Match the identifier before entering a 48-digit key. Then sign out, reboot where appropriate, and repeat the critical action with the old fallback still available. The aim is regain access to the encrypted Windows installation without destroying the only copy of the data under ordinary conditions, not a one-time success.
Do not close the incident while entering a key that does not match the identifier shown on screen remains possible. Confirm alerts, backups, ownership, and the location of recovery material. Delete exposed temporary copies, but retain the short non-secret record that explains the verified route and its stop conditions.
Action map
What to do next
| Layer | Focus | Working instruction |
|---|---|---|
| Check | 1. Photograph the recovery screen and record the key identifier and error code | A calm incident record begins with check the Microsoft account, work or school organization, printed copy, USB drive, and device-management records. |
| Action | 2. Check the Microsoft account, work or school organization, printed copy, USB drive, and device-management records | Finish “2. |
| Verify | 3. Match the identifier before entering a 48-digit key | If the key unlocks but boot still fails, use current Windows recovery options for the documented update issue. |
3. Match the identifier before entering a 48-digit key
If the key unlocks but boot still fails, use current Windows recovery options for the documented update issue. This action advances the goal to regain access to the encrypted Windows installation without destroying the only copy of the data. It also addresses the concrete failure mode “changing Secure Boot, TPM, or storage settings repeatedly and obscuring the trigger.” Capture the starting state and keep the last working device, session, or copy available until the new path has passed an independent test.
For “3. Match the identifier before entering a 48-digit key,” verify the result from a fresh session or second device. Note the exact screen, version, owner, and time without copying secrets. If the result cannot be repeated, return to the preserved state rather than stacking another irreversible change on top.
4. If the key unlocks but boot still fails, use current Windows recovery options for the documented update issue
The next move is specific: Do not clear the TPM or reinstall until data recovery and ownership are understood. Do it before any reset, deletion, migration, or firmware change connected with regain access to the encrypted Windows installation without destroying the only copy of the data. The mistake to prevent is wiping the machine before checking every legitimate recovery-key location; a screenshot of success is not enough if the recovery channel has never been tested.
Use “4. If the key unlocks but boot still fails, use current Windows recovery options for the documented update issue” as a checkpoint. Confirm the account or hardware identity, test one representative action, and record both the successful and failed behavior. Keep recovery codes, keys, or exports outside the affected device and never paste them into a search box or support chat.
5. Do not clear the TPM or reinstall until data recovery and ownership are understood
Start this stage with photograph the recovery screen and record the key identifier and error code. The purpose is regain access to the encrypted Windows installation without destroying the only copy of the data, not merely reaching the next screen. Because entering a key that does not match the identifier shown on screen, change one variable and observe the exact function that was failing before continuing.
Under “5. Do not clear the TPM or reinstall until data recovery and ownership are understood,” include a stop condition: loss of the only copy, an unmatched key identifier, unstable power during a write, an unknown administrator, or instructions for a different model. Preserve evidence and escalate at that boundary instead of improvising.
Protect the recovery route for regain access to the encrypted Windows installation without destroying the only copy of the data
A reversible workflow makes regain access to the encrypted Windows installation without destroying the only copy of the data easier to verify. Check the Microsoft account, work or school organization, printed copy, USB drive, and device-management records. Label any export with date and device, separate it from the live system, and make sure its location does not depend on the account currently being repaired.
The scenario behind “Protect the recovery route for regain access to the encrypted Windows installation without destroying the only copy of the data” is changing Secure Boot, TPM, or storage settings repeatedly and obscuring the trigger. Test the safer alternative on one account, file, or endpoint first. When it works, repeat the check after a restart or clean sign-in so cached state does not create a false pass.
A dry run for wiping the machine before checking every legitimate recovery-key location
For “A dry run for wiping the machine before checking every legitimate recovery-key location,” follow the official path: Match the identifier before entering a 48-digit key. Match the service domain, device model, hardware revision, region, and ownership type before downloading software or changing security state. Forum advice can identify a symptom but cannot verify those identifiers for you.
The risk is wiping the machine before checking every legitimate recovery-key location. Document the decision that permits the next action and the route back if it fails. On managed equipment, involve the administrator before clearing enrollment, encryption, or authentication records that may be controlled elsewhere.
What to preserve before cleanup
If the key unlocks but boot still fails, use current Windows recovery options for the documented update issue. Treat that instruction as an evidence step for regain access to the encrypted Windows installation without destroying the only copy of the data. A useful result states what was tested, from which account or network, and whether background synchronization, active sessions, metadata, or permissions also changed.
The reason for this discipline is entering a key that does not match the identifier shown on screen. Review hidden state after the visible fix: recovery addresses, forwarding rules, OAuth grants, DNS, encryption, backups, and pending queues as relevant to “What to preserve before cleanup.” Remove temporary access only after rollback is no longer needed.
How to verify the final state
A calm incident record begins with do not clear the TPM or reinstall until data recovery and ownership are understood. Tie it to “How to verify the final state” and to the intended outcome: regain access to the encrypted Windows installation without destroying the only copy of the data. Avoid a chronological diary of every click; preserve the few observations that change the diagnosis or next action.
Name the avoided error—changing Secure Boot, TPM, or storage settings repeatedly and obscuring the trigger—and the point where specialist help becomes safer than another attempt. Store the summary away from the affected device. That makes the next response start with a tested method instead of an anxious memory.
When to stop and escalate
Finish “When to stop and escalate” by proving both normal use and recovery. Photograph the recovery screen and record the key identifier and error code. Then sign out, reboot where appropriate, and repeat the critical action with the old fallback still available. The aim is regain access to the encrypted Windows installation without destroying the only copy of the data under ordinary conditions, not a one-time success.
Do not close the incident while wiping the machine before checking every legitimate recovery-key location remains possible. Confirm alerts, backups, ownership, and the location of recovery material. Delete exposed temporary copies, but retain the short non-secret record that explains the verified route and its stop conditions.
A two-minute record for the next incident
Check the Microsoft account, work or school organization, printed copy, USB drive, and device-management records. This action advances the goal to regain access to the encrypted Windows installation without destroying the only copy of the data. It also addresses the concrete failure mode “entering a key that does not match the identifier shown on screen.” Capture the starting state and keep the last working device, session, or copy available until the new path has passed an independent test.
For “A two-minute record for the next incident,” verify the result from a fresh session or second device. Note the exact screen, version, owner, and time without copying secrets. If the result cannot be repeated, return to the preserved state rather than stacking another irreversible change on top.
The final recovery rehearsal
The next move is specific: Match the identifier before entering a 48-digit key. Do it before any reset, deletion, migration, or firmware change connected with regain access to the encrypted Windows installation without destroying the only copy of the data. The mistake to prevent is changing Secure Boot, TPM, or storage settings repeatedly and obscuring the trigger; a screenshot of success is not enough if the recovery channel has never been tested.
Use “The final recovery rehearsal” as a checkpoint. Confirm the account or hardware identity, test one representative action, and record both the successful and failed behavior. Keep recovery codes, keys, or exports outside the affected device and never paste them into a search box or support chat.